
servercontrol.com.au
−0.7%
dnsvvip.com
+4.1%
mgsystem.it
+0.2%
lwsdns.com
−2.7%
smeders.nl
−1%
canaldominios.com
−0.7%
assolo.net
+0.2%
jombalak275.com
+1.4%
ad.jp
−0.2%
porkbun.com
−2.1%
markahost.com.tr
−1.6%
openhostingservice.com
+2.2%
securehost.de
+3.4%
webcloud.es
+1.3%
memset.com
+0.4%
dinahosting.com
−0.6%
webparadicsom.hu
−0.3%
webempresa.com
−0.2%
assodns.it
−1.3%
vshosting.cz
+20.3%
tarhelyszakerto.hu
−1.7%
sistemaclubedetiro.com.br
−0.8%
dns-websites.ca
−0.3%
san.psi.br
−0.3%
servercontrol.com.au
−0.7%
dnsvvip.com
+4.1%
mgsystem.it
+0.2%
lwsdns.com
−2.7%
smeders.nl
−1%
canaldominios.com
−0.7%
assolo.net
+0.2%
jombalak275.com
+1.4%
ad.jp
−0.2%
porkbun.com
−2.1%
markahost.com.tr
−1.6%
openhostingservice.com
+2.2%
securehost.de
+3.4%
webcloud.es
+1.3%
memset.com
+0.4%
dinahosting.com
−0.6%
webparadicsom.hu
−0.3%
webempresa.com
−0.2%
assodns.it
−1.3%
vshosting.cz
+20.3%
tarhelyszakerto.hu
−1.7%
sistemaclubedetiro.com.br
−0.8%
dns-websites.ca
−0.3%
san.psi.br
−0.3%
Join our newsletter
1,000+ hosting pros read it weekly. No BS, minimal ads.
Hosting jobs
All jobs →

B2B Customer Relations Team Lead
at Timeweb Cloud · Russia

Senior Director Digital Native, Customer Engineering
at Cloudflare · United States
Commercial Analyst – 12 Month Contract
at Megaport · Queensland
Technical Support Engineer – Developer Platform – Hybrid
at Cloudflare · United States
Named Account Executive, Vietnam
at Cloudflare · United States
Backed by hosting's best
Their support keeps us independent so we can help the hosting industry stay a step ahead through honest, no-BS coverage.
Latest news
See all news →
 Security
Hostinger Traces a Phoenix Server Attack to a LiteSpeed Zero-Day
Hostinger has published a report on unauthorized access to a shared hosting server in Phoenix. An attacker exploited a previously unknown flaw in LiteSpeed Web Server to break out of account isolation, gained root access and ran code or read credentials on about 400 accounts.
 Security
Roundcube Fixes 17 Flaws and Warns That 1.6 Will Be Discontinued Soon
Roundcube released versions 1.6.21 and 1.7.6 of its webmail client on November 9 with the same 17 security fixes. The announcement warns that the four-year-old 1.6 branch "will be discontinued rather soon," and cPanel and Plesk both ship 1.6.
 Security
Mittwald Traces a Breach of 56 Customer Projects to Its MCP Server
German web host Mittwald has traced a breach of customer projects to its MCP server, an interface for connecting its control panel to AI assistants. An attacker exploited a flaw on October 27, stole access tokens and went on to compromise 56 projects.
 Security
CloudLinux Rolls Out Kernel Fixes for a Local UDP Flaw Used to Crash a Server 12 Times
CloudLinux is rolling out kernel fixes for CVE-2026-98276, a Linux flaw that lets any local user crash a server. An exploit used on November 4 crashed a CloudLinux 8 server 12 times, and in separate tests the company's engineers got root access.
 Industry reports
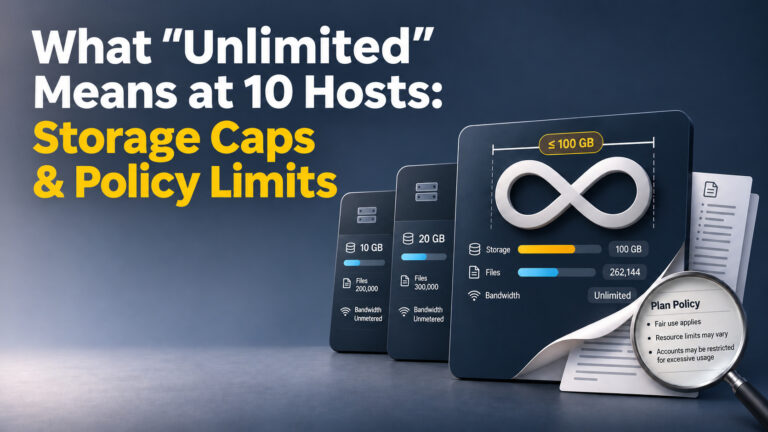
What “Unlimited” Hosting Means at 10 Major Hosts: Storage Caps and Limits Beyond the Plan Page
DreamHost's Unlimited Policy is now "Legacy," and its current plans operate "within finite limits." At 10 hosts, every entry plan has a storage figure, "unlimited" survives mainly on bandwidth, and many of the limits that matter sit in help pages.
 Security
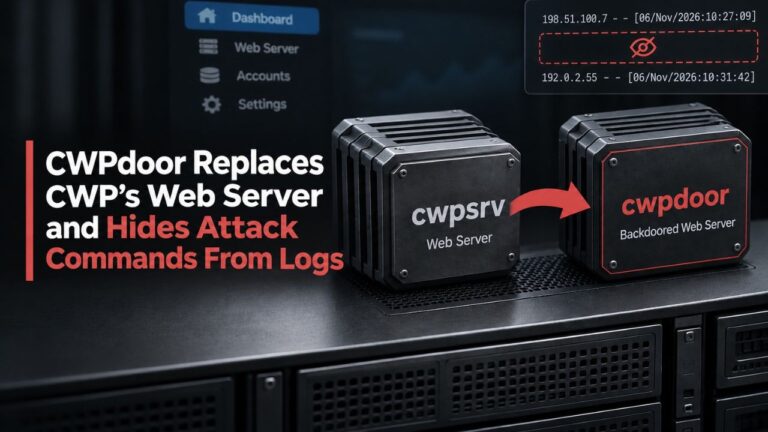
CWPdoor Replaces Control Web Panel’s Web Server and Hides Attack Commands From Logs
Attackers are replacing cwpsrv, the web server behind the free hosting panel Control Web Panel, with a backdoored copy. The backdoor stays dormant until it receives a signed request, then runs the attacker's command and keeps that request out of the access logs.
Browse the full archive
814 articles, filterable by category & tag
Hosting M&A Desk
with Konrad & Łukasz · M&A advisors
Hosting M&A Desk
Sell or acquire a hosting company with expert guidance. We connect sellers with 250+ verified buyers worldwide. Private deals, real valuations, and full support – from strategy to closing.
250+Verified buyers
100%Private & discreet
webhosting.today Podcast
Honest conversations with founders, CEOs and engineers shaping the hosting industry.
Latest
23 Sep 2026
The Future of Managed Hosting (Suhaib Zaheer, Cloudways / DigitalOcean)
with Konrad Keck
Episode
26 Aug 2026
Is Bluehost Still a Hosting Company? – (Sachin Puri, BlueHost, Network Solutions)
with Konrad Keck
Episode
8 Jul 2026
AI Will Kill Traditional Agencies (Brent Weaver, E2M Solutions)
with Konrad Keck
Episode
8 Apr 2026
When Should You Sell Your Hosting Business? M&A Q&A #1
with Konrad Keck
Listen on


Browse all episodes →
Stay ahead of the hosting industry
Be where 1,000+ hosting pros already are. News, M&A, market moves, security alerts — weekly, no bull.